Evidence-linked QA is the practice of connecting every regulated testing decision to durable proof: requirements, test design, execution records, defects, approvals, environments and release rationale. For regulated products, the goal is not merely to show that checks passed. It is to make the path from product risk to release decision understandable to an auditor, reviewer or future incident team.
To build evidence-linked testing, define what evidence must exist for each risk, link requirements to test cases and results, preserve artifacts in controlled storage, and record why release decisions were made. The workflow should make auditability a normal by-product of testing rather than a last-minute documentation project.
Why Evidence Matters Beyond Pass or Fail
A pass/fail result answers one narrow question: did a specific check meet its expected outcome at a specific moment? Regulated testing has to answer broader questions: what requirement was checked, why was the test sufficient, what product version was used, who reviewed the result, what exceptions were accepted, and whether the evidence can still be trusted later.
This is why evidence-linked QA treats test artifacts as part of the product safety and compliance record. The supplied TRACE-TEST framework record describes an evidence-linked software quality assurance approach for AI-augmented testing in regulated platforms, emphasizing the need to connect testing activity with supporting proof rather than isolated outputs in its Zenodo record. NIST’s SAMATE program also places software assurance in a context where testing, tool evaluation and evidence about software behavior matter to security and reliability claims through its software assurance work.
The practical implication is simple: a test that cannot be traced, reproduced or explained is weak evidence. It may still help a developer, but it is not strong enough to support a regulated release decision on its own.
What Counts as Test Evidence?
Test evidence is any controlled artifact that helps prove what was tested, how it was tested, what happened, and how the team interpreted the outcome. Strong evidence is complete, attributable, time-bound, tamper-resistant and linked to the requirement or risk it supports.
- Requirement and risk records: user needs, regulatory requirements, hazard analyses, security requirements, acceptance criteria and change requests.
- Test design artifacts: test cases, charters, data sets, automation code, expected results, coverage notes and review comments.
- Execution records: run IDs, timestamps, product build identifiers, tester or service account identity, environment details and execution status.
- Observed outputs: logs, screenshots, API responses, database snapshots, device readings, trace files, generated reports and monitoring records.
- Defect and deviation records: bug reports, reproduction steps, severity assessments, retest evidence, waivers and accepted-risk rationale.
- Approval and decision logs: sign-offs, release readiness notes, unresolved issue lists and reasons for proceeding or stopping.
Evidence does not need to be excessive. In fact, uncontrolled evidence piles can become harder to audit than missing evidence. The goal is to capture enough proof to support the risk, not to archive every incidental file a tool can produce.
How Do You Link Requirements to Results?
Traceability is the connective tissue of regulated testing. It shows the path from a requirement or risk to test design, execution result, defect handling and final decision. Without traceability, teams end up relying on memory, spreadsheet archaeology or individual tool experts when an auditor asks a direct question.
What traceability should a QA lead require?
At minimum, each regulated requirement should have an identifier, owner, status, risk classification, linked verification method, linked test evidence and review state. Each test result should point back to the requirement it supports and forward to any defect, deviation or release decision that depends on it.
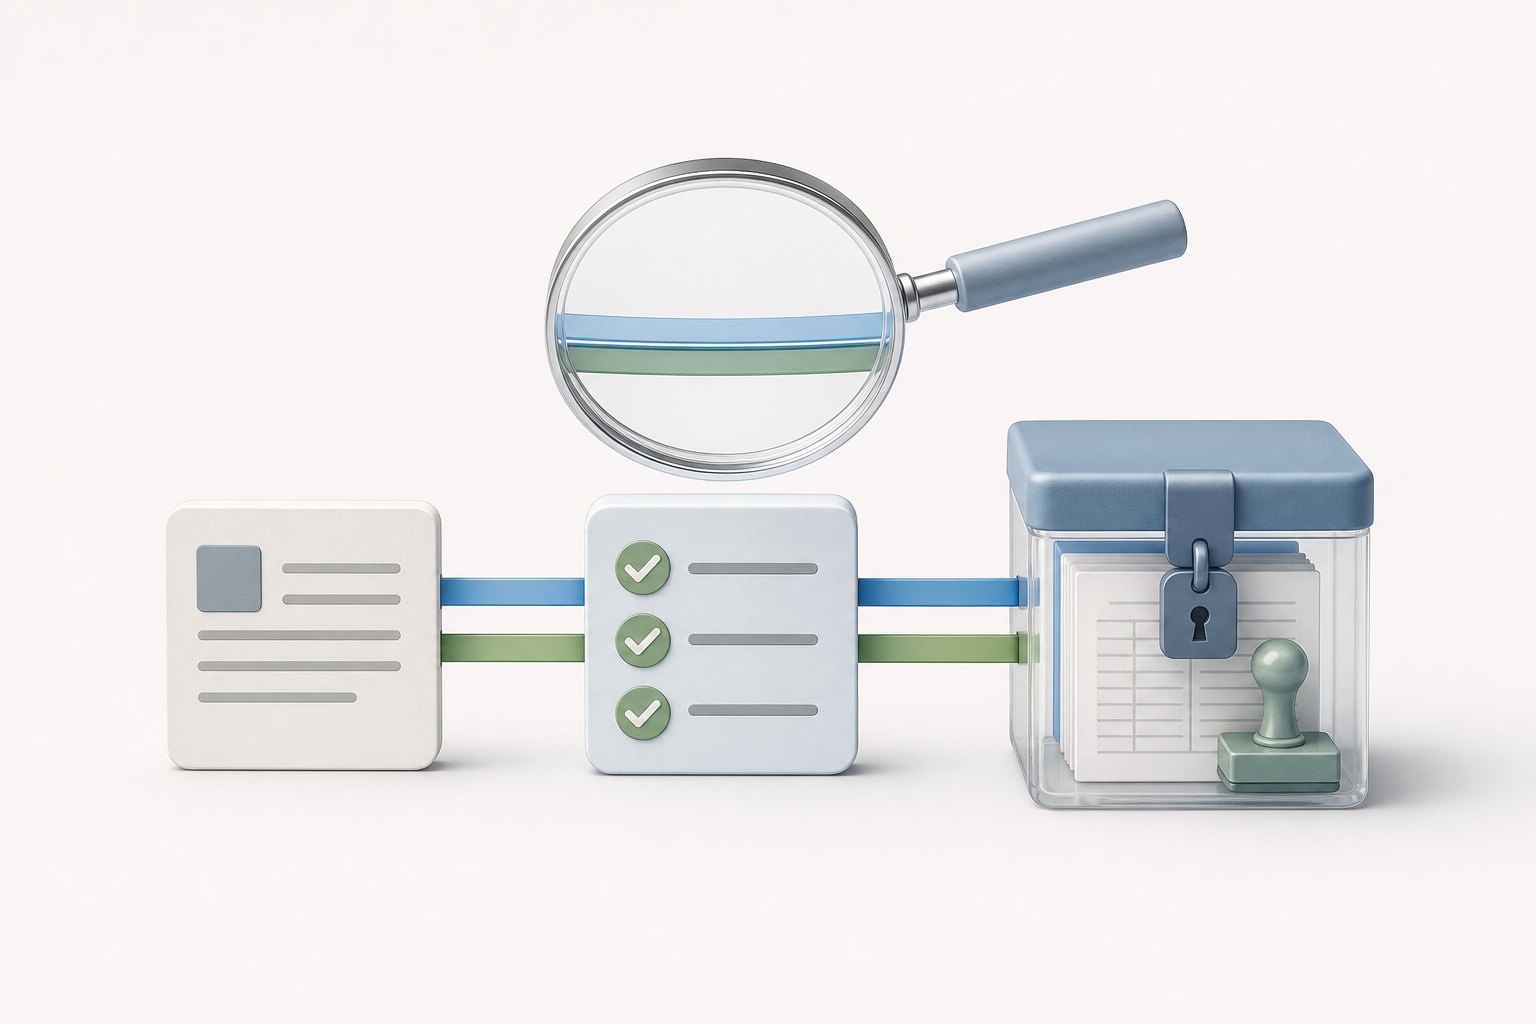
A useful traceability chain looks like this: requirement to risk to test case to execution run to artifact bundle to defect or approval to release decision. If a link is missing, the team should know whether that is a process gap, a tool integration gap or an intentional exception.
| Approach | Best fit | Audit strength | Common weakness |
|---|---|---|---|
| Manual traceability matrix | Small products or early process maturity | Clear when maintained carefully | Easy to become stale after frequent changes |
| ALM or test management workflow | Teams with formal requirements and release gates | Strong when permissions and history are controlled | Can hide evidence in tool-specific screens |
| Evidence manifest as code | Automation-heavy teams and CI pipelines | Strong when stored with immutable artifacts | Requires discipline around identifiers and metadata |
| Artifact repository only | Supplemental storage for logs, reports and binaries | Useful for preservation | Weak if artifacts are not linked to requirements |
How much evidence is enough?
The right amount of evidence depends on product risk, regulatory expectations, system complexity and the consequences of failure. A low-risk usability change may need a lightweight review record and targeted regression evidence. A safety-critical workflow, security control or data-integrity function may need reviewed requirements, controlled test scripts, repeatable test data, execution logs, defect closure evidence and formal release approval.
Use risk to scale the evidence. Do not apply the heaviest evidence package to every change, because teams will eventually bypass or dilute the process. A sustainable quality system makes the most important evidence mandatory and the optional evidence clearly optional.
Audit-Friendly Workflows That Do Not Slow Every Release
Audit readiness improves when evidence is captured during normal work. If QA engineers have to reconstruct test proof after release, the process is already fragile. A better workflow defines evidence checkpoints inside planning, test design, execution, triage and release review.
- Plan with evidence in mind: identify regulated requirements, risk level, required verification method and expected evidence before testing begins.
- Review test design before execution: confirm that test cases or charters cover the requirement and that expected results are objective.
- Capture execution metadata automatically: attach product version, environment, run ID and executor identity wherever possible.
- Link defects immediately: connect failed results to defect records, retest runs and final closure evidence.
- Record decisions while they are made: document risk acceptance, scope exclusions and release readiness in a decision log.
- Freeze evidence at release: preserve the exact artifact set that supports the release, including known limitations.
For teams building broader operating models, evidence-linked QA should be part of the quality system rather than a separate compliance overlay. SQAExperts’ guide to a scalable quality engineering framework is a useful companion when aligning test governance with agile delivery. Team habits matter too; a high-performance quality engineering team needs shared standards for what “done” means when evidence is required.
Tooling and Storage Patterns for Durable Evidence
Evidence-linked QA can be implemented with many tool stacks, but the storage pattern should be deliberate. Regulated teams commonly need controlled access, retention rules, version history, reviewer attribution and a way to export evidence without losing context. A screenshot in a chat thread is not durable evidence unless it is captured into a controlled record with the right metadata.
One useful pattern is an evidence manifest: a small structured file that lists the requirement, build, environment, test run, artifact locations and review state. The manifest does not replace the test management system. It creates a portable map of evidence that can be stored with release artifacts.
evidence_record:
  requirement_id: REQ-142
  risk_level: high
  product_version: 4.8.0-rc3
  change_request: CR-7719
  verification_method: automated regression plus exploratory confirmation
  test_runs:
    - run_id: ci-2026-10-14-087
      status: passed
      environment: validated-staging-eu
      executor: qa-automation-service
      artifacts:
        - type: junit-report
          location: artifact-store/releases/4.8.0-rc3/ci-087/results.xml
        - type: api-log
          location: artifact-store/releases/4.8.0-rc3/ci-087/api-log.json
    - run_id: exploratory-qa-219
      status: passed-with-observation
      environment: validated-staging-eu
      executor: named-tester-record
      artifacts:
        - type: session-notes
          location: evidence-store/REQ-142/session-notes.pdf
  linked_defects:
    - defect_id: BUG-9081
      final_status: closed
      retest_run: ci-2026-10-14-087
  decision:
    release_recommendation: approve
    rationale: required behavior verified and prior defect retested
    reviewer: qa-lead-record
    review_status: approved
This example is intentionally simple. In a real environment, the artifact locations should resolve to controlled storage, and the identities should map to authenticated users or service accounts. If checksums, digital signatures or immutable storage are part of your quality system, include them consistently rather than only for exceptional releases.
What Can Go Wrong?
Evidence programs often fail for organizational reasons, not because teams lack tools. The most common failure is treating auditability as documentation work performed after engineering work is complete. That creates gaps, delays and low-confidence records.
Why do evidence programs become unusable?
They become unusable when the team captures too much low-value material, stores it in too many places or uses identifiers inconsistently. Another common failure is allowing test cases to change after execution without preserving the tested version. If a reviewer cannot tell which test definition produced a result, the evidence is ambiguous.
- Stale traceability: requirements change, but tests and evidence links are not updated.
- Uncontrolled attachments: files are saved without ownership, versioning or retention classification.
- Weak environment proof: results do not show which build, configuration, data set or dependency version was used.
- Unreviewed automation: automated checks produce reports, but no one verifies that the checks still match the requirement.
- Decision gaps: the team knows why a release was approved, but the rationale exists only in meetings or chat.
Can AI-augmented testing use evidence responsibly?
Yes, but AI-generated or AI-assisted testing needs explicit evidence boundaries. If a tool proposes test cases, generates automation or summarizes failures, preserve the human-reviewed output and the decision record that accepted it. The supplied TRACE-TEST record is specifically framed around evidence-linked QA for AI-augmented testing in regulated platforms as described in the Zenodo entry, which reinforces the importance of connecting AI-assisted activity to auditable proof.
Do not treat an AI-generated test as self-justifying evidence. The evidence should show what requirement the test covers, who reviewed it, what version was executed, what output was observed and how the result influenced a decision. For regulated teams, human accountability remains part of the record even when tools accelerate test creation or analysis.
Review and Retention Policy
A review policy defines who can approve evidence, what reviewers must check and what happens when evidence is incomplete. A retention policy defines how long evidence is kept, where it is stored, how it can be retrieved and when it can be disposed of. Both policies should be specific enough to guide daily work but flexible enough to scale by risk.
Reviewers should check trace completeness, requirement coverage, test version, execution context, defect closure and decision rationale. They should not merely confirm that a report exists. A report with missing build information or broken requirement links may look complete while failing the auditability test.
Retention should account for product life, regulatory obligations, customer commitments and incident investigation needs. Avoid promising universal retention if storage, access control and retrieval cannot support it. It is better to define clear evidence classes, such as release evidence, exploratory support material, CI diagnostics and incident records, then assign retention and access rules to each class.
Key Takeaways
- Evidence-linked QA connects requirements, risks, tests, results, defects and release decisions into one auditable chain.
- Pass/fail status is not enough for regulated testing unless the result is tied to product version, environment, test definition and review context.
- Risk should determine the depth of evidence, so high-impact requirements receive stronger proof without overwhelming every change.
- Audit readiness is strongest when evidence is captured during normal workflows instead of reconstructed after release.
- Controlled storage, consistent identifiers and preserved test versions are essential for trustworthy test evidence.
- AI-assisted testing can support regulated teams only when generated outputs are reviewed, linked and preserved as part of the evidence record.